IT Services by Industry
Sectors don't differ in the technology they buy so much as in the rules they buy it under. A patch window on a production line isn't a patch window on a laptop fleet, and a privacy breach at a law firm is a conduct problem before it's a security one. Pick your sector and we'll name the regime, then the service that answers it.
Where the rules change the architecture.
Seven sectors, each with the regimes that bind it and the services that answer them. No sector case studies yet, so no page here claims any.

Financial Services and Fintech
OSFI's technology and cyber risk rules set what an examiner will ask to see.
- OSFI B-13
- OSFI B-10
- OSFI E-23
- Provincial credit union regimes
- CCSPA (Bill C-8)
- AI Governance E-23 covers AI models from 2027-05-01. Model inventory and approval records, built.
- Third-Party Risk Management B-10 expects you to evidence it, not assert it.
- SOC 2 Compliance Services The report your enterprise customers ask for before signing.
- ISO 27001 Certification Support Where an international counterparty prefers the ISO route.
- Penetration Testing Testing at the cadence your regulator and your customers expect.
- Identity and Access Management Segregation of duties, provable per transaction.
- Cloud Security B-13 doesn't exempt anything because it's managed.
- Managed Security Services (MSSP) Detection that runs after hours, which is when it matters.
- Cybersecurity Consulting Where the three B-13 domains meet, and where most gaps sit.

Healthcare and Life Sciences
Health information sits under provincial privacy law, and your IT provider is usually the custodian's agent.
- PHIPA
- Provincial equivalents
- PIPEDA
- Breach notification
- PIPEDA Compliance The federal baseline, and where provincial health law takes over.
- Privacy Impact Assessment (PIA) Expected before a new system touches health information.
- Backup and Disaster Recovery A clinician who can't reach a record is a patient safety issue.
- Security Awareness Training Health records are the highest-value target in the country.
- Identity and Access Management Who opened which chart, provable, because someone will ask.
- Endpoint Management Shared workstations and devices that never leave the ward.
- Managed Security Services (MSSP) Monitoring that understands what a health record is worth.
- Virtualization Services Clinician access from anywhere without records leaving.

Legal
Solicitor-client privilege decides how a firm can handle its data.
- Law Society obligations
- Solicitor-client privilege
- PIPEDA breach notification
- Quebec Law 25
- Security Awareness Training Phishing a legal assistant is cheaper than attacking your firewall, and it works more often.
- Backup and Disaster Recovery Matter files carry retention obligations that outlive the client relationship.
- Managed Security Services (MSSP) Monitoring by people who understand what privilege means.
- Identity and Access Management Who can open which matter, provable after the fact.
- PIPEDA Compliance The notification duty, documented before you need it.
- Quebec Law 25 Compliance Separate thresholds the moment you hold a Quebec client's file.
- Endpoint Management Devices that leave the office with client files on them.
- Virtualization Services Remote access to the files without the files leaving.
Manufacturing and Industrial
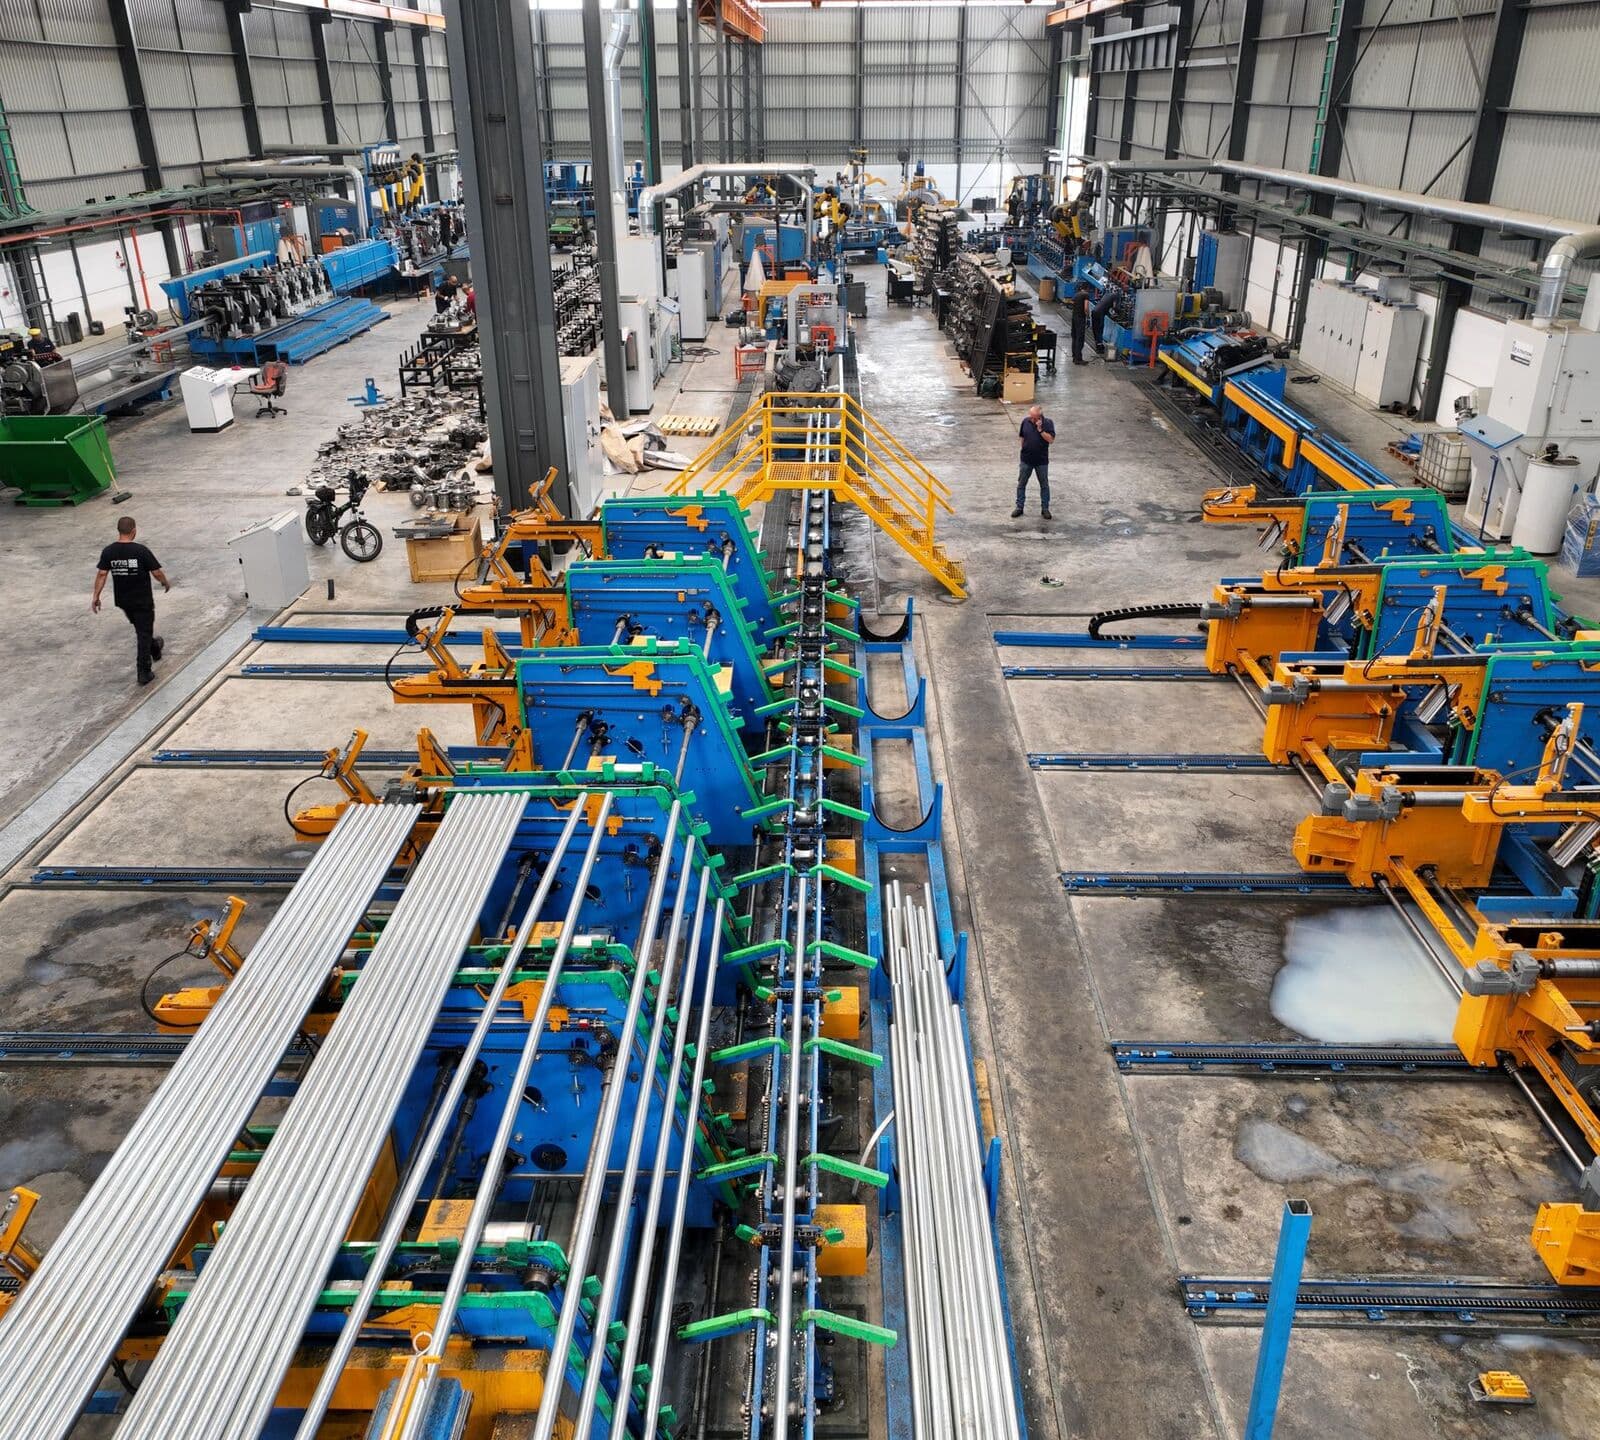
A production line can't stop for a patch window, so changes have to fit the schedule.
- OT and IT convergence
- Patch windows
- Legacy equipment
- ISO 22301
- Network Security Segmentation between plant floor and corporate, so one doesn't reach the other.
- Enterprise Networking A network designed for machines that don't reboot on demand.
- IT Support Services Shifts don't stop at five and neither does the line.
- Backup and Disaster Recovery A production line stopped is revenue per minute, not per day.
- ISO 22301 Business Continuity The continuity certification your larger customers ask for.
- Endpoint Management Including the machines you can't patch, isolated properly instead.
- Co-Managed IT Your plant engineer knows the floor. We cover the rest.
- Vulnerability Management Which of the machines you can't patch actually matter, ranked.
- Cisco ISE Network access control for devices that can't run an agent.
Mining, Energy and Utilities
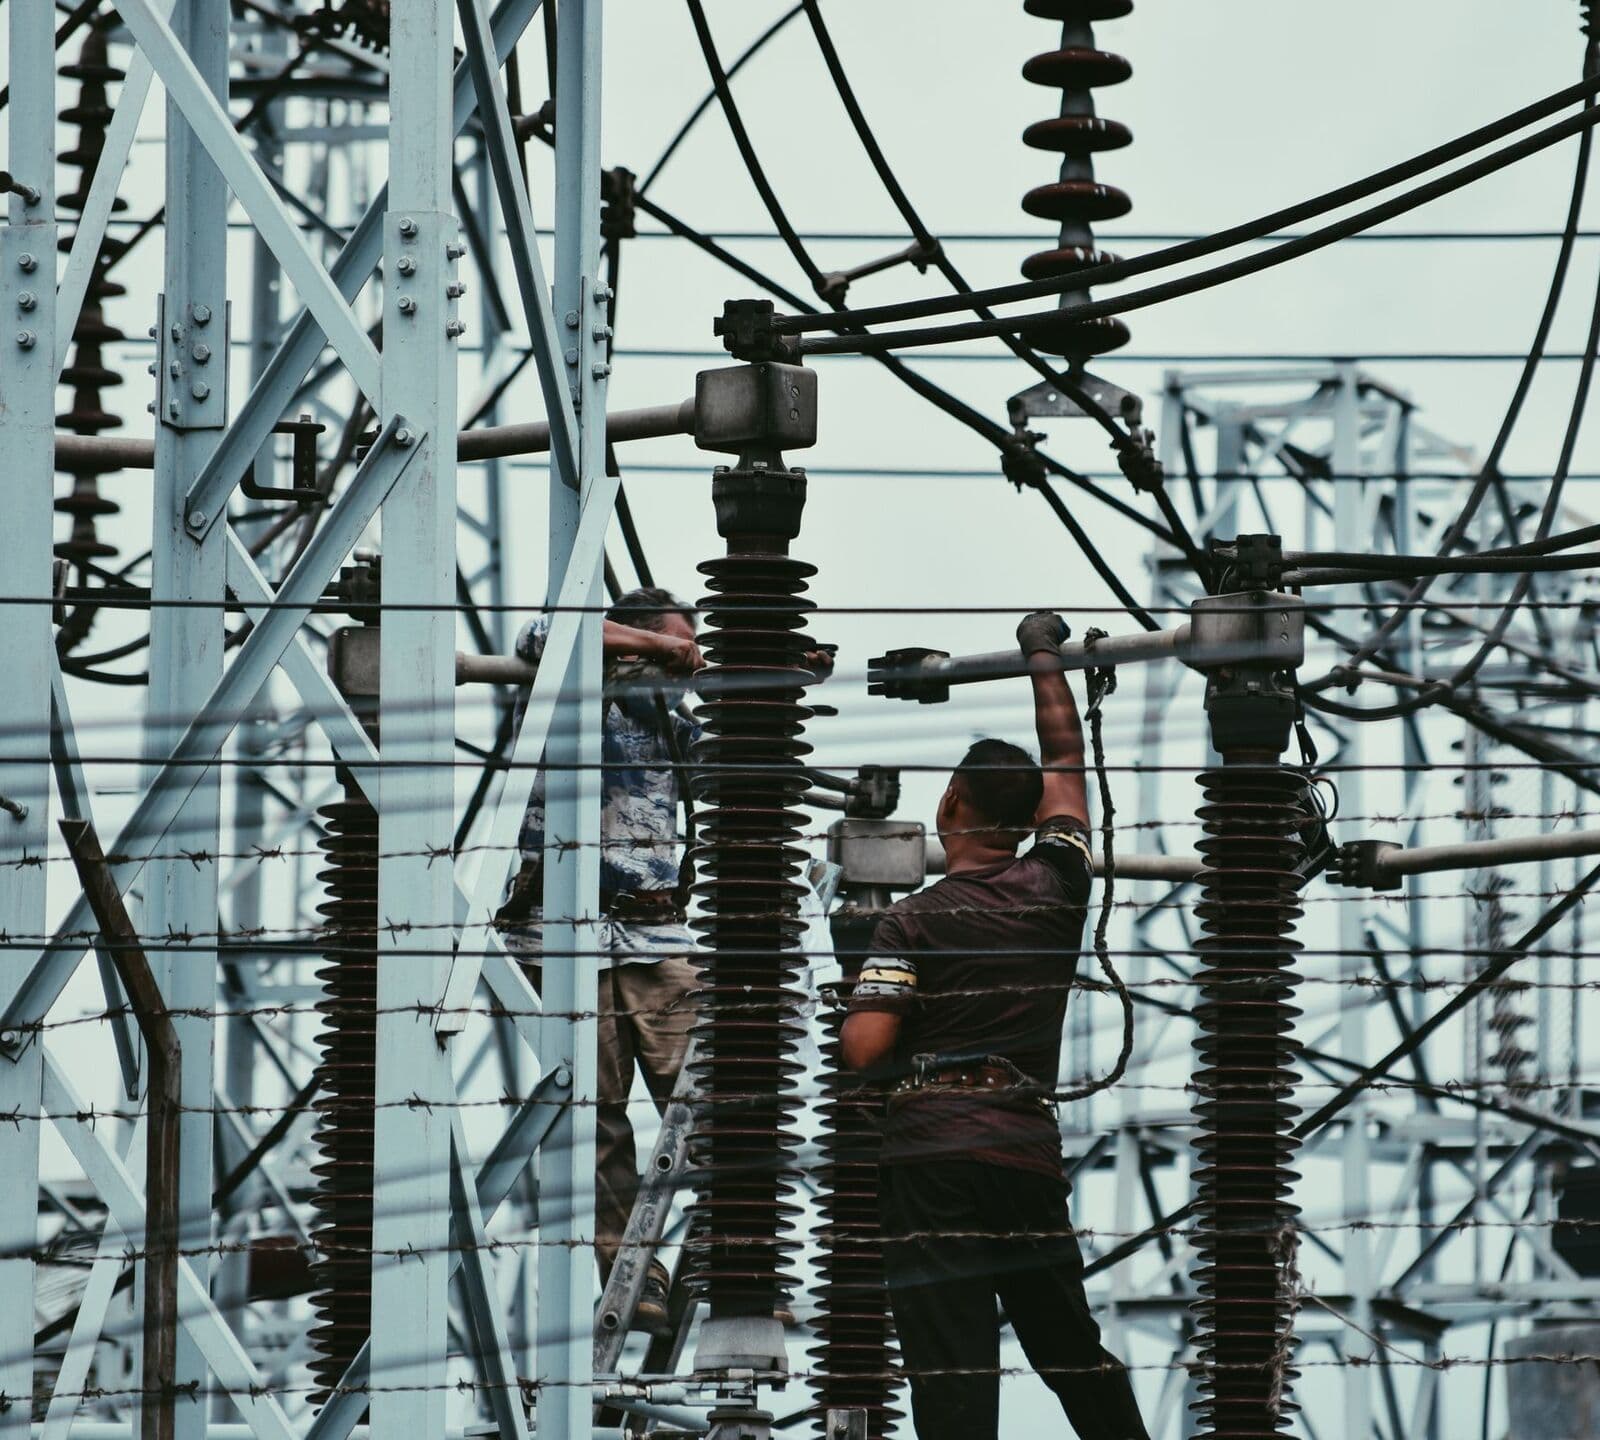
SCADA networks and remote sites can't go offline, so changes are planned around them.
- Bill C-8 and the CCSPA
- SCADA and ICS
- Remote-site connectivity
- ISO 22301
- SD-WAN Solutions Remote sites on whatever link you can get, managed centrally.
- Bill C-26 Readiness Where you'd stand when Part 2 is brought into force.
- Network Security Keeping the control network separate from everything else.
- Threat Risk Assessment (TRA) The assessment a regulator will eventually ask to see.
- IT Support Services Sites run around the clock in places nobody visits at night.
- Backup and Disaster Recovery Remote sites have no local IT to restore from a shelf.
- ISO 22301 Business Continuity Continuity planning that accounts for physical isolation.
- Managed Security Services (MSSP) Monitoring where you can't take a system offline to investigate.
- Enterprise Networking Kit specified for the environment, not the catalogue.

Government and Public Sector
Protected A, B and C data handling decides where the work can run and who can touch it.
- Protected A, B and C
- ITSG-33, and ITSP.10.033
- CPCSC
- PIPEDA and the Privacy Act
- Bill C-8
- CPCSC Certification Support The certification federal supply-chain contracts increasingly require.
- Privacy Impact Assessment (PIA) Mandatory before a new programme touches personal information.
- Threat Risk Assessment (TRA) The TRA that ITSG-33 expects, against the catalogue that's current.
- Bill C-26 Readiness Where you'd stand if Part 2 is brought into force.
- On-Premise and Sovereign AI For data that cannot leave Canadian soil, whatever the vendor promises.
- Data Centre Services Canadian-resident infrastructure, documented for an auditor.
- Managed Security Services (MSSP) Monitoring with a Canadian SOC and Canadian log retention.
- PIPEDA Compliance The baseline that applies regardless of classification.
Defence and Aerospace
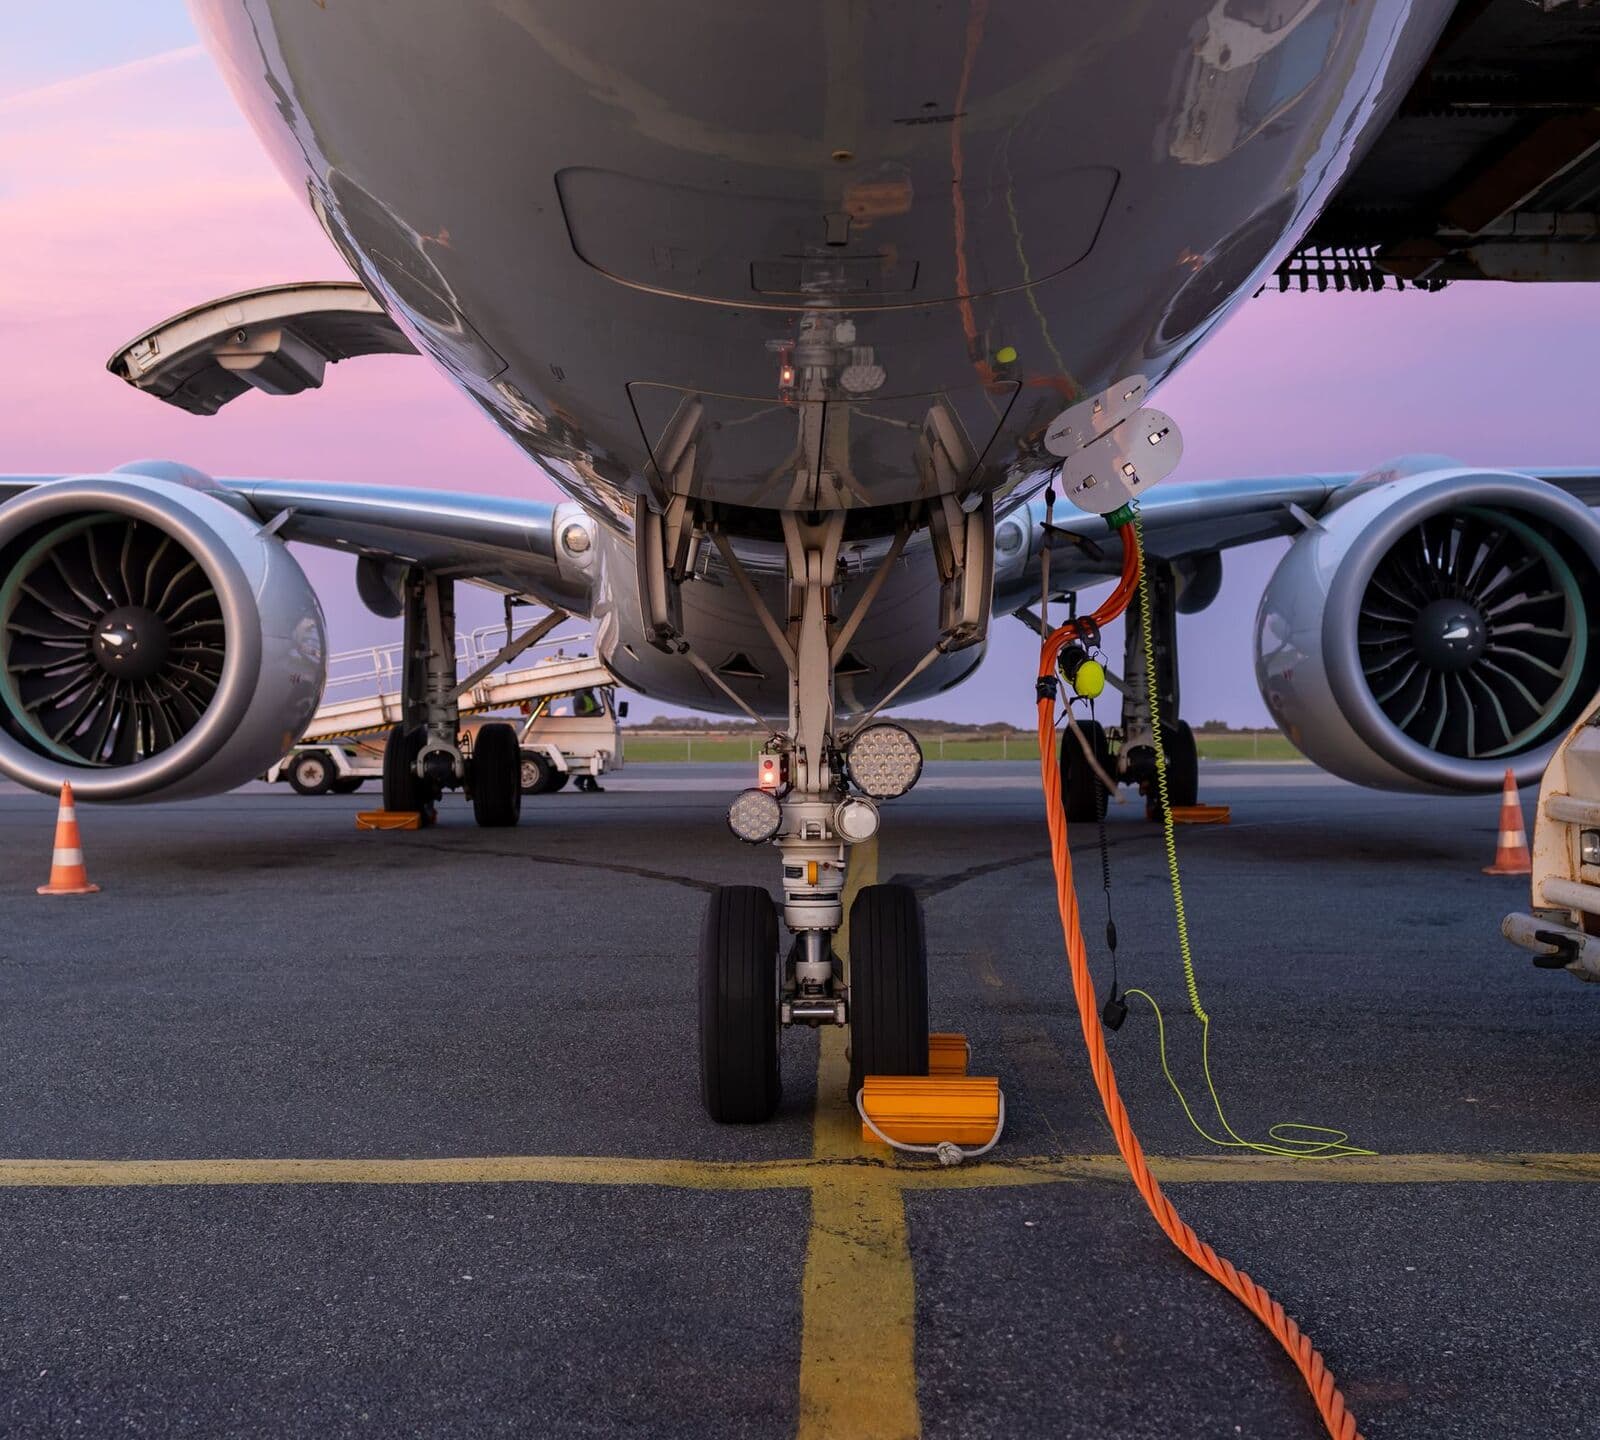
Controlled goods rules, CMMC and the flow-down from your prime set what a supplier can do.
- CMMC
- NIST SP 800-171
- ITAR and the Controlled Goods Program
- CPCSC
- Flow-down from your prime
- CMMC Compliance The level your contract names, assessed against the real control set.
- NIST Cybersecurity Framework The control mapping underneath CMMC, done once and reused.
- CPCSC Certification Support For the Canadian side of the same supply chain.
- On-Premise and Sovereign AI Controlled data that can't cross a border, including into a model.
- Third-Party Risk Management Your subcontractors inherit your obligations. Prove they meet them.
- Identity and Access Management Controlled-goods access has to be provable per person, per document.
- Network Security Segmentation between controlled and general environments.
- Data Centre Services Infrastructure inside the boundary you're allowed to use.
