Managed security services with the authority to act, not just alert
Trusted by







Managed security services, three pillars, one operator.
One Canadian team writes the detections, holds the authority to act, and shows its working.
Detection engineering
Rules tuned to your estate and your normal, reviewed monthly. A vendor default pack is a starting point, not a service.
Response authority
What we can disable, isolate, or kill without calling you, agreed in writing before go-live, so nobody debates permission during an attack.
Evidence and tuning
False positives tracked as a number we report to you, coverage gaps named rather than hidden, and reporting an auditor can read.
Does Managed Security Services work the same way in every industry?
No. The Managed Security Services work is the same craft in every sector, but the conditions around it are not. In financial services that means OSFI's technology and cyber risk rules; in healthcare, provincial health privacy law; and in legal, Law Society duties and solicitor-client privilege. We keep the service and change the part that bends.

Detection that runs after hours, which is when it matters.
OSFI B-13. Technology and cyber risk across three domains: governance, technology operations and resilience, and cyber security. It binds federally regulated institutions, and only those.

Monitoring that understands what a health record is worth.
PHIPA. Ontario's health privacy act, with its own definition of a custodian and its own duties for the agents acting on a custodian's behalf. Your IT provider is usually an agent.

Monitoring by people who understand what privilege means.
Law Society obligations. Confidentiality and competence duties reach the technology you practise with, and the vendors who touch client information. The firm is expected to have assessed the provider, which means the provider should arrive with the answers.
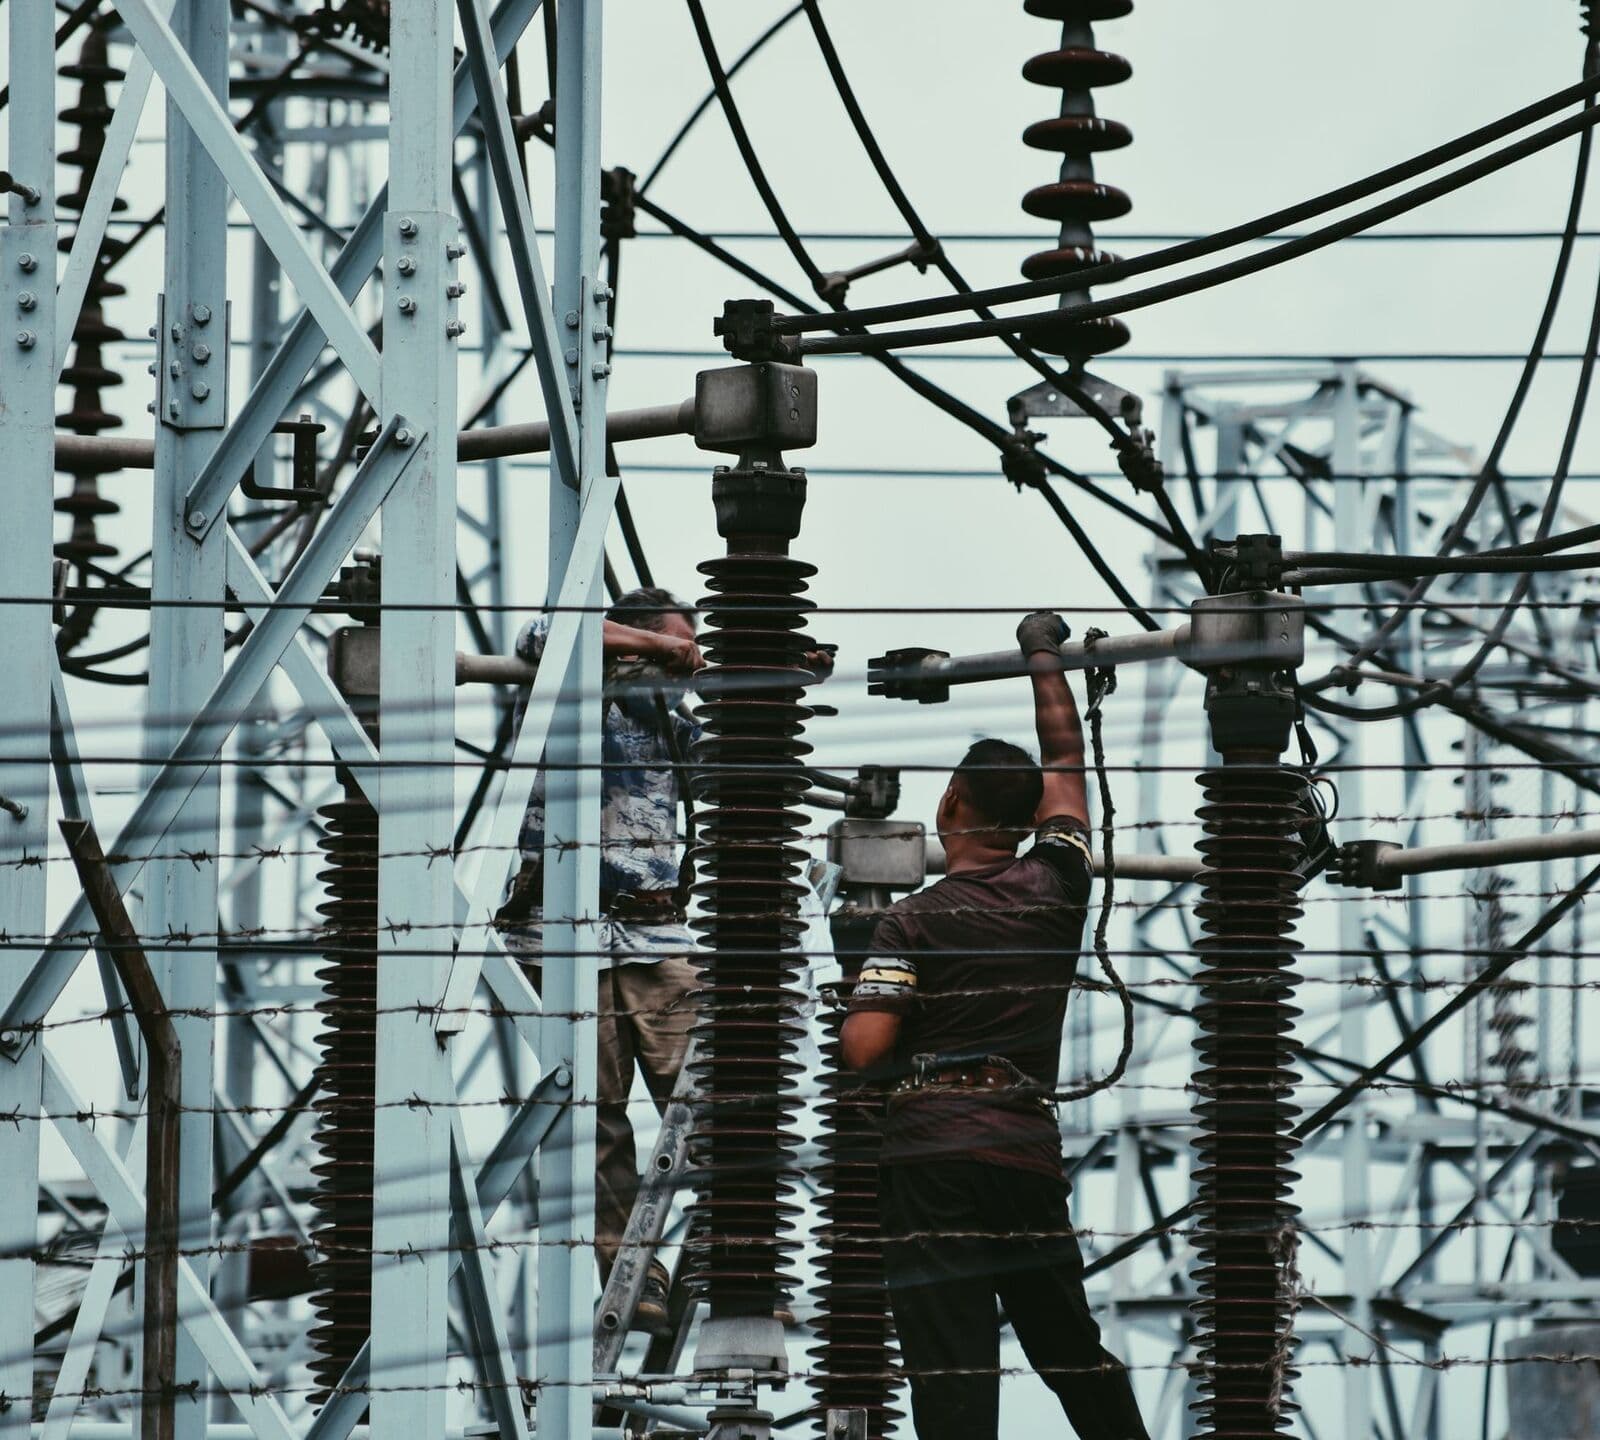
Monitoring where you can't take a system offline to investigate.
SCADA and ICS. Availability outranks confidentiality here, and you often can't take a system offline to investigate what happened on it.

Monitoring with a Canadian SOC and Canadian log retention.
Protected A, B and C. Each level changes where the data can physically live, who can reach it, and what you have to prove about both. Most files turn on Protected B, and most disagreements turn on what counts as reaching it.
What do you need from Managed Security Services?
Tell us who you are and what you're working on. A senior engineer reads your message before replying, so the first answer is a real read on scope, risk and timing, within an hour, 24/7. Nothing here is a commitment, and we'll tell you plainly if we're not the right fit.
Your request
- Service
- Managed Security Services
What happens next
- A senior engineer replies within an hour, 24/7, never an SDR.
- We book a 30-minute call to listen, sketch options, and flag risks.
- You get a scoped statement of work within 3 business days.
Call the 24/7 line
+1 514-465-1584Managed security services in Canada, made real.
Almost every quote in this category means something different. That's the buyer's real problem.
The words are the mess, so ask the 3am question.
MSSP, MDR, SOC as a service, co-managed SIEM, and managed EDR get used interchangeably, and two quotes with matching headline prices can differ by whether anyone is allowed to touch your systems. So ask the question that separates them: at 3am, can they isolate a host and disable an account, or do they send an email and wait? That single answer sorts the market faster than any feature grid, and almost nobody publishes it.
Why speed is the whole product.
Canadian breaches took an average of 205 days to identify and contain in 2026, up 6%, at a record average cost of $7.11M. Organisations with AI in their security operations detected in 124 days and contained in 57. Those without took 154 and 71 (source: IBM, 2026-07-29). That's 44 days of difference, and it's bought with tuned detections and standing authority, not with a bigger tool.
Where the risk actually sits.
Risk sits in two places. Alert volume nobody triages, which is how a real detection dies in a queue of 400 false positives, and log coverage with holes in it. We track the false-positive rate as a number we report to you, because an untuned service degrades into noise inside a quarter. On residency: your logs can stay in Canada, which matters because PIPEDA applies to whatever your telemetry captures, and log data is rarely as anonymous as people assume.

Want a Senior IT Consultant's Read on Your Setup?
Tell us what you run today and what keeps breaking. A senior SMEnode engineer replies within an hour with a first read on scope, risk and timing. No sales handoff.
Request a consultHow our MSSP and 24/7 security monitoring work runs.
Four steps, and step 02 is the one other providers skip. Most onboarding goes straight from contract to log shipping, which produces coverage nobody has verified and permissions nobody has agreed. We do the paperwork first: what we watch, what we're allowed to do about it, and who we wake if the answer is nobody. That conversation is uncomfortable once and saves the argument that otherwise happens mid-incident, when it costs hours.
Engagement phases
Phases 01 to 04
Map the telemetry
What logs exist, what they miss, and what it costs to close each gap. You see the coverage map, including the parts we can't see, before signing.
Agree the authority
Written, specific, and signed. Which accounts we can disable, which hosts we can isolate, and the threshold that triggers a phone call rather than a ticket.
Engineer the detections
Rules written against your estate and your baseline, tested for noise before they go live. Vendor default packs are a starting point, not a service.
Tune it monthly
False-positive rate, missed-coverage review, and what changed in your estate. Detections rot as environments change, so this is the work, not an add-on.
Managed security services questions, answered straight.
Answers first, including when this is the wrong purchase. An architect takes the call, not a salesperson.
Where this work connects.
These disciplines share the same senior team and tend to land together. Follow the thread to the next one.
- SecurityPenetration TestingCanadian penetration testing services with written scope, reproducible findings, and a retest after you fix.
- SecurityNetwork SecurityCanadian network security services built by CCIEs, with segmentation, access control and firewall policy actually enforced.
- SecuritySecurity Awareness TrainingCanadian security awareness training run as a programme, with phishing simulation, coaching, and an auditor-ready record.