Endpoint management in Canada, run by the engineers who built it
Trusted by







Endpoint management, three pillars, one operator.
One Canadian team owns the tooling, the patching, and the proof.
Unified endpoint management
Laptops, desktops, phones, and tablets under one policy set, usually Microsoft Intune, sometimes Jamf.
Patch management
Operating system and third-party patching on a tested schedule, with a rollback path when a vendor ships a bad one.
Endpoint compliance and reporting
Canadian CCIE Security engineers prove device posture to your auditor, not just to your dashboard.
Does Endpoint Management work the same way in every industry?
No. The Endpoint Management work is the same craft in every sector, but the conditions around it are not. In healthcare that means provincial health privacy law; in legal, Law Society duties and solicitor-client privilege; and in manufacturing, production lines that can't stop for a patch window. We keep the service and change the part that bends.

Shared workstations and devices that never leave the ward.
PHIPA. Ontario's health privacy act, with its own definition of a custodian and its own duties for the agents acting on a custodian's behalf. Your IT provider is usually an agent.

Devices that leave the office with client files on them.
Law Society obligations. Confidentiality and competence duties reach the technology you practise with, and the vendors who touch client information. The firm is expected to have assessed the provider, which means the provider should arrive with the answers.
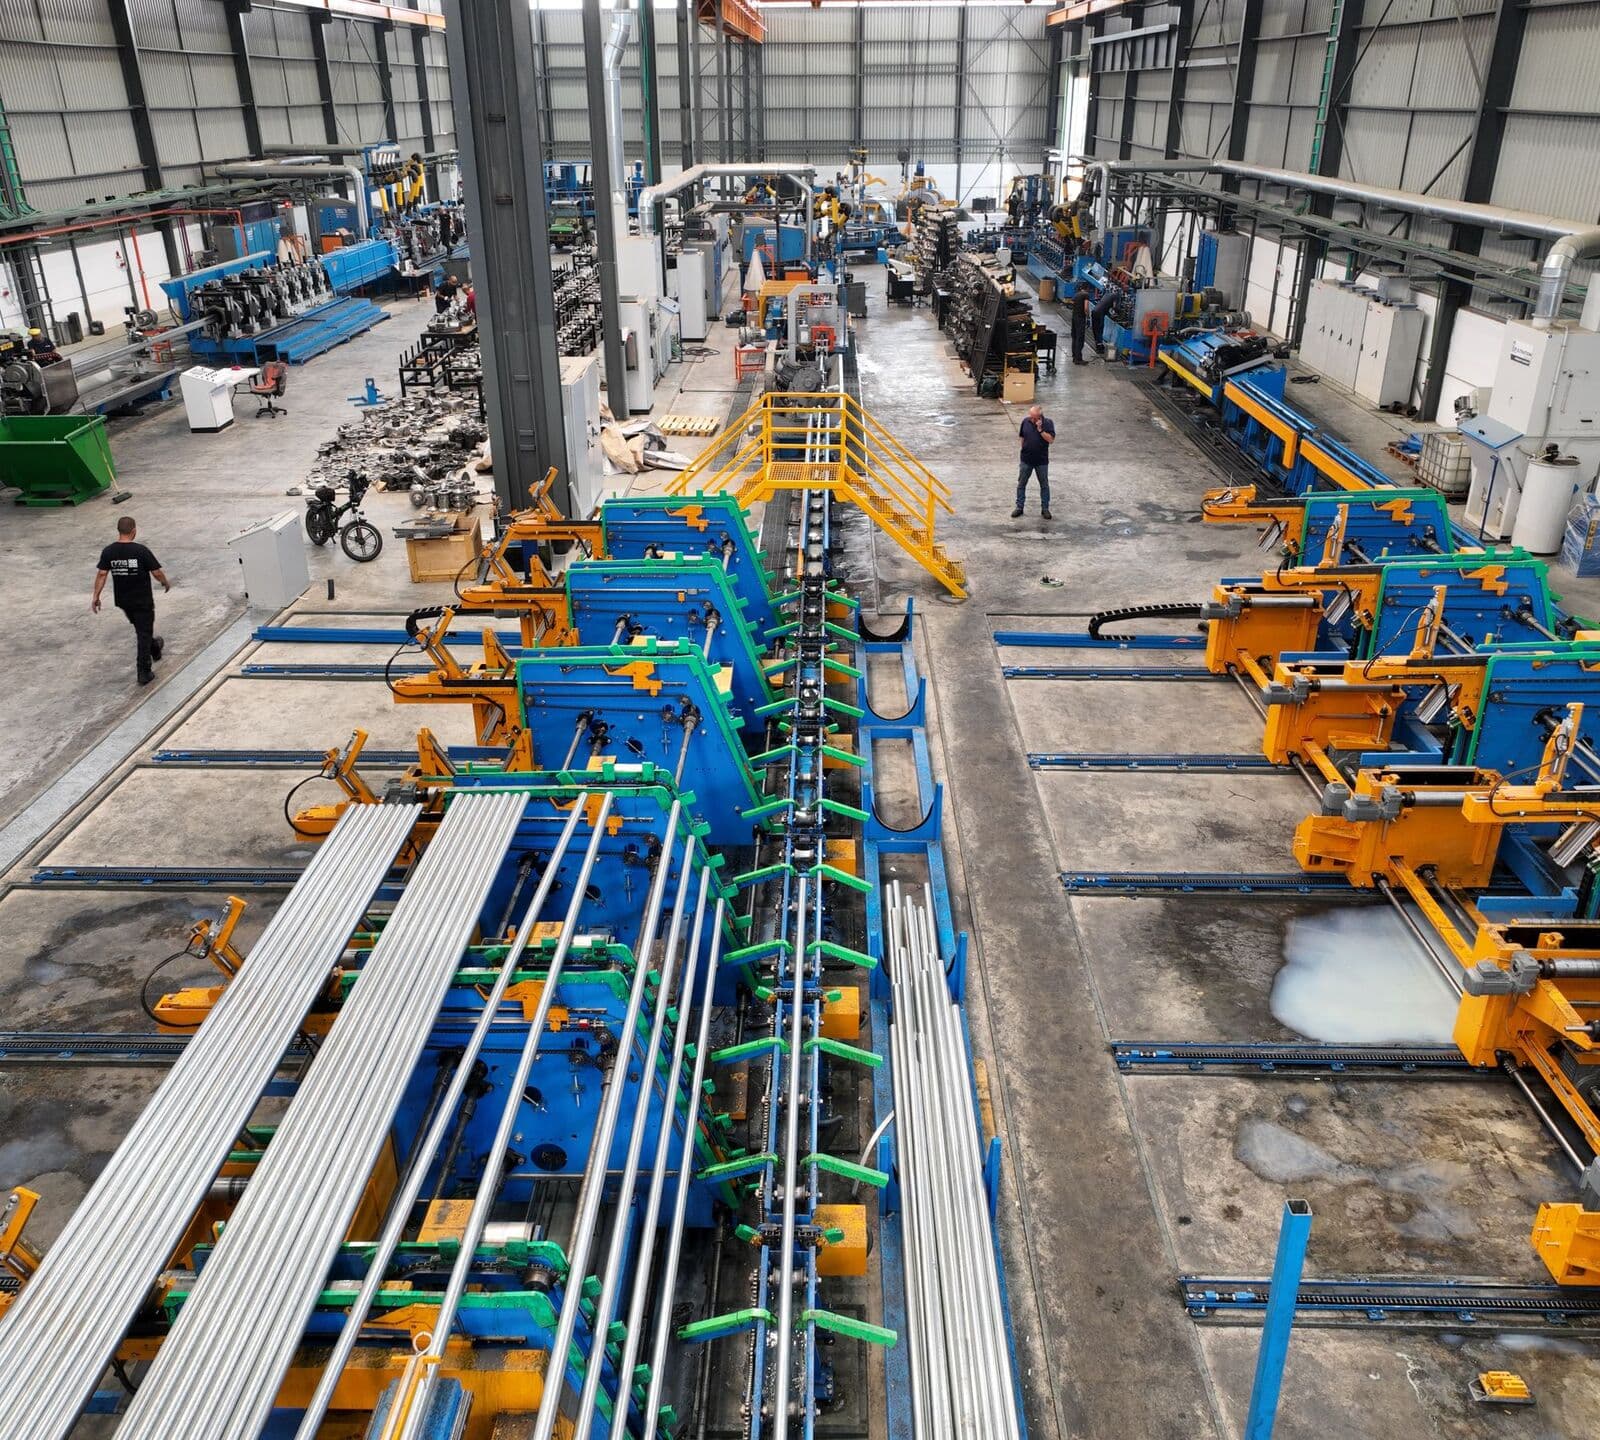
Including the machines you can't patch, isolated properly instead.
OT and IT convergence. A flat network between plant and office is the common failure, and segmentation is the fix. It's a design problem, not a purchase.
What do you need from Endpoint Management?
Tell us who you are and what you're working on. A senior engineer reads your message before replying, so the first answer is a real read on scope, risk and timing, within an hour, 24/7. Nothing here is a commitment, and we'll tell you plainly if we're not the right fit.
Your request
- Service
- Endpoint Management
What happens next
- A senior engineer replies within an hour, 24/7, never an SDR.
- We book a 30-minute call to listen, sketch options, and flag risks.
- You get a scoped statement of work within 3 business days.
Call the 24/7 line
+1 514-465-1584Endpoint management in Canada, made real.
I run this practice, so this is written by the engineer who'll own your fleet, not a product page.
Endpoint management, defined the way we build it.
Endpoint management is the process of enrolling, configuring, patching, and proving the state of every device on your network, from one place. Good means three things: you know what you own, every device is on a patch schedule someone tests, and you can produce evidence of both. Most device management services stop at the first. Unified endpoint management only earns the name when phones and laptops sit under the same policy, not two consoles nobody reconciles.
How we work.
Here's how we work. We inventory first and always find surprises: contractor laptops, a shelf of unenrolled spares, phones belonging to people who left. Then we build policy in rings, test on IT first, and only then push to the business. Most of your risk isn't the tool. It's the device nobody knew existed and the patch nobody tested before it broke Excel for 200 people on a Monday.
What you already pay for.
On tooling, we're honest about what you already pay for. Microsoft Intune Plan 1 is already included with Microsoft 365 E3, E5, F1, F3, and Business Premium, so most Canadian teams already own an MDM and don't run it (source: Microsoft, 2026). Standalone Intune Plan 1 runs 8 dollars per user per month if you need it separately. From July 2026 Microsoft moved several advanced endpoint capabilities into E3 and E5, including Endpoint Privilege Management and Remote Help (source: Microsoft, 2026). We'd rather turn on what you're licensed for than sell you another console.

Want a Senior IT Consultant's Read on Your Setup?
Tell us what you run today and what keeps breaking. A senior SMEnode engineer replies within an hour with a first read on scope, risk and timing. No sales handoff.
Request a consultHow an endpoint management rollout runs.
We sequence the work so nothing breaks in front of your users. Week one is inventory, not deployment. We find every device, work out which ones are actually in use, and reconcile against what HR and procurement think you own. From there we build policy in rings and prove each one before it moves. Every SMEnode engagement runs this way, across Canada.
Engagement phases
Phases 01 to 04
Inventory and reconcile
We find every device, enrolled or not, and match it against payroll and purchase records. Out of it comes a real asset list, the gap between it and your console, and a written policy baseline. This step alone usually finds the unmanaged machines.
Build and pilot
We build configuration, compliance, and patch policies, then pilot on IT's own devices. Nothing reaches a user until it's survived the team that can debug it.
Roll out in rings
Enrolment goes in waves, lowest risk first. Each ring has to hold for a set period before the next one starts. A bad policy hits ten people, never a thousand.
Run and prove
We hold the patch schedule, watch compliance drift, and give you a monthly report showing device count, patch state, and exceptions with reasons. That report is what your auditor wants, and it's what most fleets can't produce.
Endpoint management questions, answered straight.
These are the questions IT managers actually ask us. Answers are from the engineer who runs the fleets.
Where this work connects.
These disciplines share the same senior team and tend to land together. Follow the thread to the next one.
- ManagedCo-Managed ITCo-managed IT services in Canada that add senior engineers to your internal IT team, not replace it.
- SupportManaged Service DeskManaged help desk and service desk in Canada: tier 1 to tier 3 support, ITIL process, identity checks before resets and a monthly report on causes.
- ManagedBackup and Disaster RecoveryBackup and disaster recovery in Canada built on immutable copies and restores we test on a schedule.