Cybersecurity Company in Vancouver
Search cyber security vancouver and you'll find job boards, college programmes and a Reddit thread about careers. Search cybersecurity companies in vancouver and it's mostly directories. This page is neither. It covers cyber security for Vancouver businesses: the assessment, the controls, the monitoring, and the evidence a regulator asks for after something goes wrong. CCIE-led, run from North York. Looking for a course? The questions at the bottom point you somewhere better.
Trusted by







It breaks into three jobs, and many providers only sell one. Find out what's really there: the devices, the exposure, and which controls work rather than which ones a policy lists. Fix it: segmentation, identity, endpoint, email, patching, and backups you can restore. Then watch it, with overnight monitoring and a rehearsed incident plan. In BC that last job depends on who you are. A credit union is expected to call BCFSA within 24 hours, while PIPA sets no notice deadline at all.
Seven cyber security services we run in Vancouver
Each one has its own page: what we scope, how we run it and what you get back. Start with the one you need, or ask us to run them together.
Managed Security Services (MSSP)
A Canadian managed security service provider that agrees what it can do at 3am before go-live.
View servicePenetration Testing
Canadian penetration testing services with written scope, reproducible findings, and a retest after you fix.
View serviceNetwork Security
Canadian network security services built by CCIEs, with segmentation, access control and firewall policy actually enforced.
View serviceSecurity Awareness Training
Canadian security awareness training run as a programme, with phishing simulation, coaching, and an auditor-ready record.
View serviceThreat Risk Assessment (TRA)
Canadian threat risk assessment mapped to the federal control catalogue that took effect in March 2026.
View serviceIdentity and Access Management
Canadian identity and access management built on the platform you already own, with joiners and leavers handled.
View serviceVulnerability Management
Canadian vulnerability management that ranks by real exploitation, then tracks every finding to closed.
View service
When does cyber security in Vancouver need hands?
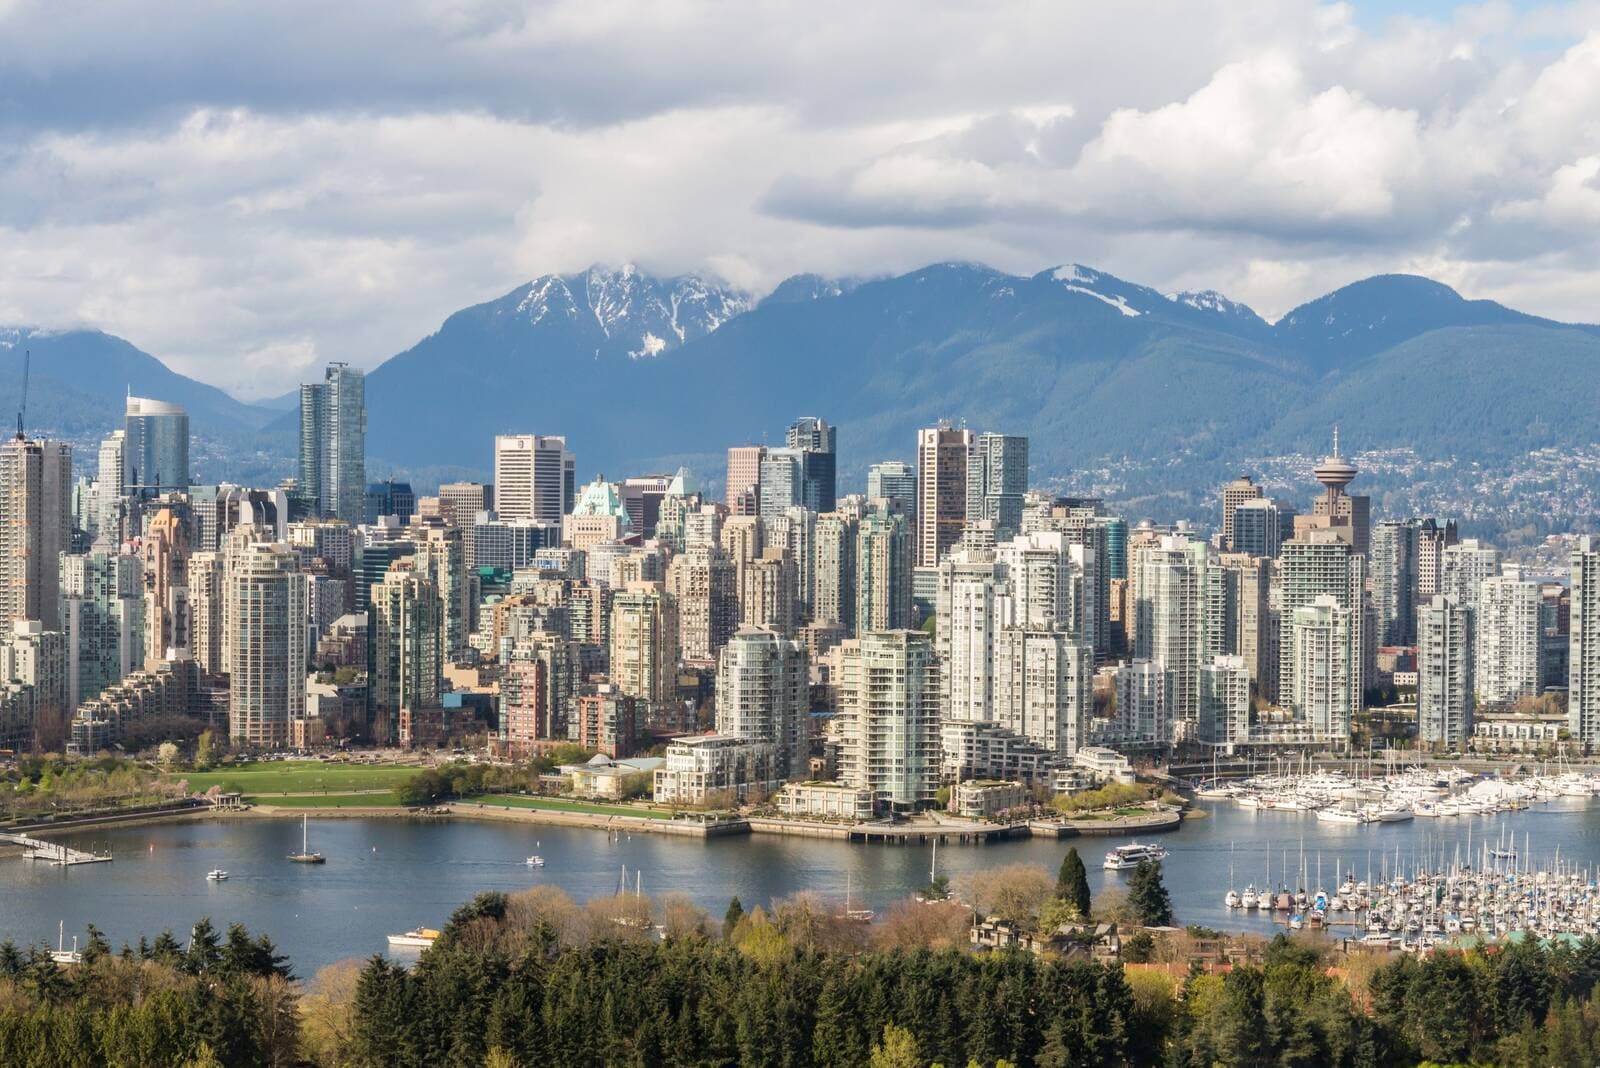
Less than people expect, more than any dashboard implies. Detection and response have to run remotely, because an attacker won't wait for a visit. What needs a person is finding out what's actually plugged in: the assessment walk, segmentation work in a warehouse or studio, and the rare incident where a cable must be pulled. Across Vancouver, Burnaby and Surrey we plan those visits with you, and remote containment starts straight away.
What needs somebody there
- Walking each site to find the devices nobody listed
- Segmenting a warehouse or studio network without any downtime
- Physically isolating an infected machine during an incident
- A tabletop exercise, which works better around a real table than on video
What runs the same from anywhere
- Monitoring, detection and overnight alerts
- Access reviews and patching, plus endpoint and email controls
- The written assessment and the remediation plan
- Incident records, reporting timelines and access logs, kept current
Assessment and exercise visits are planned around your change windows, in advance.

Want a Senior IT Consultant's Read on Your Setup?
Tell us what you run today and what keeps breaking. A senior SMEnode engineer replies within an hour with a first read on scope, risk and timing. No sales handoff.
Request a consultWho does the work
The architect who runs your assessment also writes the design and remains your contact afterwards. In security, the tool matters less than whether you can still reach the person who designed your segmentation when an attacker starts testing it.
What we take over
- What you have now:
A penetration test report from years ago, with most of the findings still open
What the engagement leaves:An assessment ranking real exposure above things that are merely untidy
- What you have now:
One flat network, because segmentation kept slipping to next year
What the engagement leaves:A segmentation design, and agreed change windows to put it in
- What you have now:
Alerts so noisy that nobody on the team reads them any more
What the engagement leaves:Alerting tuned to your environment, so an overnight page signals a real attack
- What you have now:
An incident plan that still names someone who left
What the engagement leaves:An incident process with named people, the BC reporting clocks that apply, and a rehearsal
- What you have now:
Cyber insurance forms answered with guesses about your controls
What the engagement leaves:Insurance questionnaire answers backed by evidence from controls that actually run
This is the shape of a Vancouver cyber security engagement, not a single client.
What do you need from Cyber Security Services?
Tell us who you are and what you're working on. A senior engineer reads your message before replying, so the first answer is a real read on scope, risk and timing, within an hour, 24/7. Nothing here is a commitment, and we'll tell you plainly if we're not the right fit.
Your request
- Service
- Cyber Security Services
What happens next
- A senior engineer replies within an hour, 24/7, never an SDR.
- We book a 30-minute call to listen, sketch options, and flag risks.
- You get a scoped statement of work within 3 business days.
Call the 24/7 line
+1 514-465-1584