IT Company Ottawa
Search it company ottawa or it services ottawa and half of page one is hiring lists. This isn't one. SMEnode is a CCIE-led IT company working across the National Capital Region, and the senior engineer who designs your network is the one who builds it and answers when it breaks. We work to ITSG-33 controls and the CPCSC gate that started landing in defence contracts this summer. Enterprise networking, security, cloud and AI.
Trusted by







What makes IT work in Ottawa different?
The National Capital Region holds 155,505 federal public servants, and Kanata North holds 802 companies and 63,000 jobs in what its own association calls Canada's largest technology park. Two buyers, one city, and almost nothing in common. The federal one can't sign with you until you clear a gate, and since this summer that gate has a name: CPCSC Level 1, introduced on 2026-04-14 and now appearing in select defence contracts.
Federal departments, agencies, and the firms that hold their contracts. National Capital Region IT work starts at the control set
802 companies in Canada's largest technology park. Semiconductors, photonics, cybersecurity, SaaS. A Kanata IT company scaling past 50 staff hits the same wall
The Quebec side of the federal footprint. Gatineau IT services carry Law 25 on the same file as PIPEDA
Mid-market business, professional services, distribution
Defence supply chain and the contractors around it
We don't have an Ottawa office, and here's what that means
Our engineers work out of North York. For the National Capital Region that's a scheduled on-site visit, not a same-morning one. We'd rather you read that here than discover it during an incident.
- Monitoring and response run 24/7, from the same team either way.
- Design, build, migration and audit work is remote-first for everyone, including the firms with a Slater Street address.
- The work a federal supplier actually needs from us, control mapping, evidence, an ITSG-33 profile and a CPCSC submission, is a document set. Nobody drives it over.
Monitoring runs 24/7. On-site visits are booked, and the contract says how fast.
What we run in Ottawa
- 01Cyber SecurityCyber security for Ottawa organisations that have to prove it. Assessment, monitoring and evidence mapped to ITSG-33. No Ottawa office, we say so.View service
- 02Managed IT ServicesManaged IT for Ottawa and the NCR. ITSG-33 control mapping, CPCSC, screening answered straight, bilingual desk, 24/7. No Ottawa office, and we say so.View service
- 03IT ConsultingIndependent IT consulting for Ottawa businesses and federal suppliers. Inventory, architecture, cost baseline and a straight read of which gate applies.View service
- 04IT SupportOttawa IT support for federal-contract work. ITSG-33 control mapping, CPCSC, a bilingual desk and 24/7 monitoring. No Ottawa office, and we say so.View service
- 05Government ITWhat a federal IT supplier actually has to clear: organisation screening, TBIPS, ITSG-33 profiles and CPCSC. Written for suppliers, not departments.View service
The engineers who cover Ottawa
Not a bench you are quoted and never meet. These are the people who take the call.
A senior engineer takes the call
A 30-minute call with a senior engineer who reads the contract's security requirements first. If CPCSC Level 1 or an ITSG-33 profile is the gate, you hear that on the call.
The person who designed it, builds it
The person who designs your network writes the control evidence as part of the build. That evidence is a document set, so it never waits for a site visit.
Monitoring runs 24/7
On-site visits are booked, and the contract says how fast.
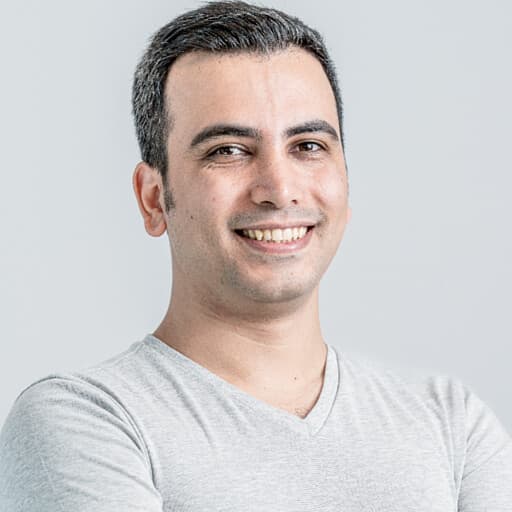
Saeid Ghobadi
Founder and Principal Architect
CCIE Data Center
Works out of North York, on site in the National Capital Region by scheduled visit
View profile
Industries we run in Ottawa
Federal departments and agencies
ITSG-33 is the control catalogue everything else is measured against, and it's where a security assessment either starts or stalls. We build the profile, map what you run against it, and write the evidence in the form an assessor will accept.
Defence supply chain
CPCSC Level 1 arrived on 2026-04-14 and started appearing in select defence contracts this summer. Certification isn't needed to bid yet, only on award, which is the window suppliers are in right now. Thirteen requirements. Most of the work is proving what you already do.
Technology companies in Kanata North
802 companies, and the ones scaling past 50 staff hit the same wall: a network built by whoever was free, and a customer security questionnaire they can't answer. We fix the second by fixing the first.
Gatineau and cross-river operations
An office on the Quebec side puts Law 25 on the same file as PIPEDA, with different consent rules and different breach thresholds. One estate, two regimes. It's a data-residency and logging problem before it's a legal one.
Questions Ottawa buyers ask
How is this different from the MSP you have?
Four things worth checking, and worth putting to anyone else quoting you.
Who answers
A named architect who already knows your topology, because they drew it.
Instead of a shared inbox, then whoever is free on tier one.
The gate
We read the contract's security requirements before the design, so the control evidence is a by-product of the build.
Instead of an assessment response assembled after an award is already at risk.
What we say about distance
No Ottawa office, said on the page, with on-site terms written into the contract.
Instead of a local claim that turns into a four-hour window when something breaks.
What you sign
A count of the estate first. It usually makes the number smaller.
Instead of a per-seat tier sheet priced before anyone looked.
