Organizational change management for the systems we deploy
Trusted by







Organizational change management, three pillars, one operator.
One Canadian team deploys the system and gets it used, so technology adoption is our problem too, not a hand-off to someone else.
Change readiness
We find who'll resist, what they'll lose, and which workflow you're about to break. The change readiness pass runs before the rollout starts, and it sometimes changes the rollout.
Training and enablement
Role-based sessions on your configuration, not a vendor's demo tenant. Each role gets a live session, a recording, and a one-page reference, so training and enablement matches the system people actually log into.
Adoption measurement
We watch real usage for thirty days after launch and fix what people work around. Logins and feature use, not attendance sheets.
Does Organizational Change Management work the same way in every industry?
No. The Organizational Change Management work is the same craft in every sector, but the conditions around it are not. In manufacturing that means production lines that can't stop for a patch window; in healthcare, provincial health privacy law; and in legal, Law Society duties and solicitor-client privilege. We keep the service and change the part that bends.
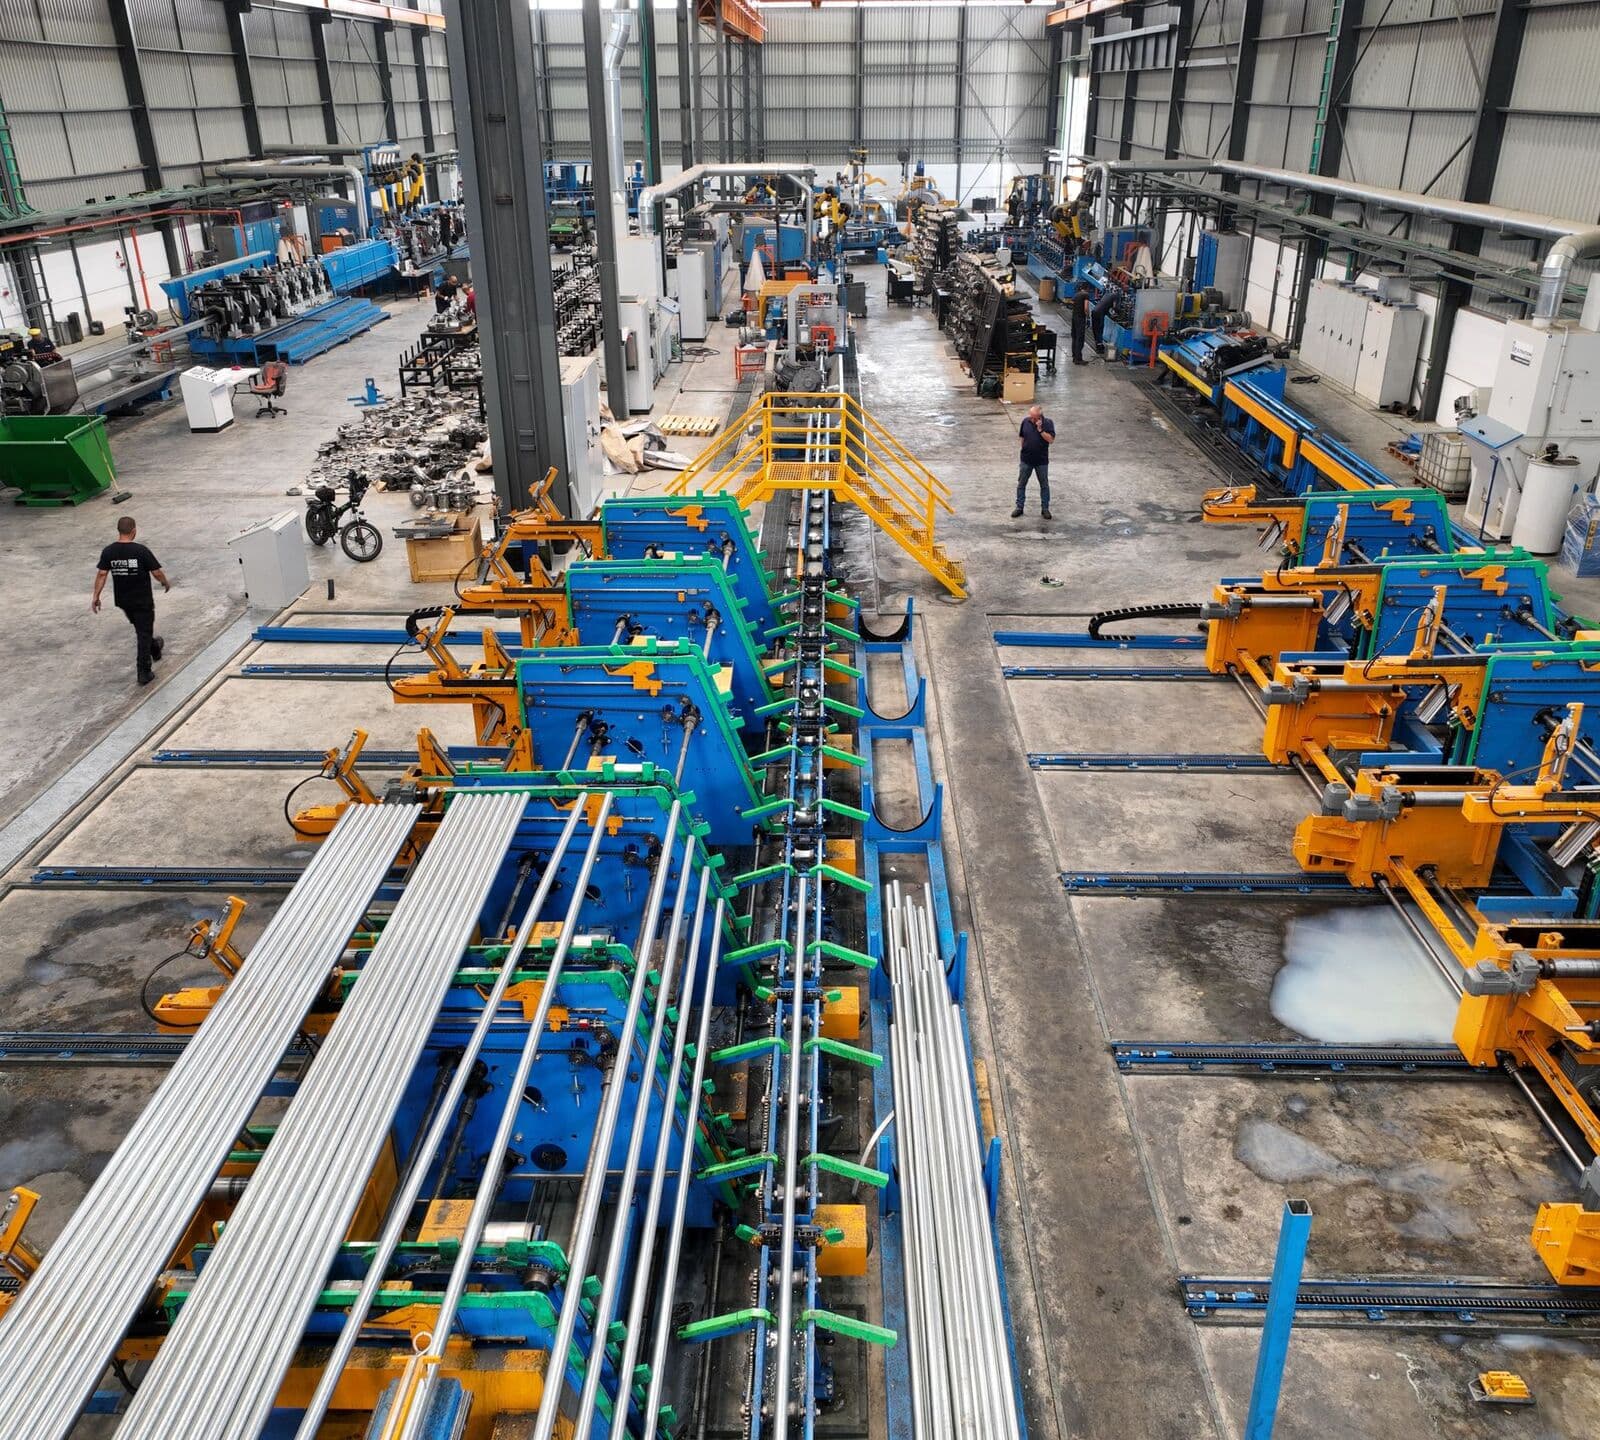
A production line can't stop for a patch window, so changes have to fit the schedule.
OT and IT convergence. A flat network between plant and office is the common failure, and segmentation is the fix. It's a design problem, not a purchase.

Health information sits under provincial privacy law, and your IT provider is usually the custodian's agent.
PHIPA. Ontario's health privacy act, with its own definition of a custodian and its own duties for the agents acting on a custodian's behalf. Your IT provider is usually an agent.

Solicitor-client privilege decides how a firm can handle its data.
Law Society obligations. Confidentiality and competence duties reach the technology you practise with, and the vendors who touch client information. The firm is expected to have assessed the provider, which means the provider should arrive with the answers.
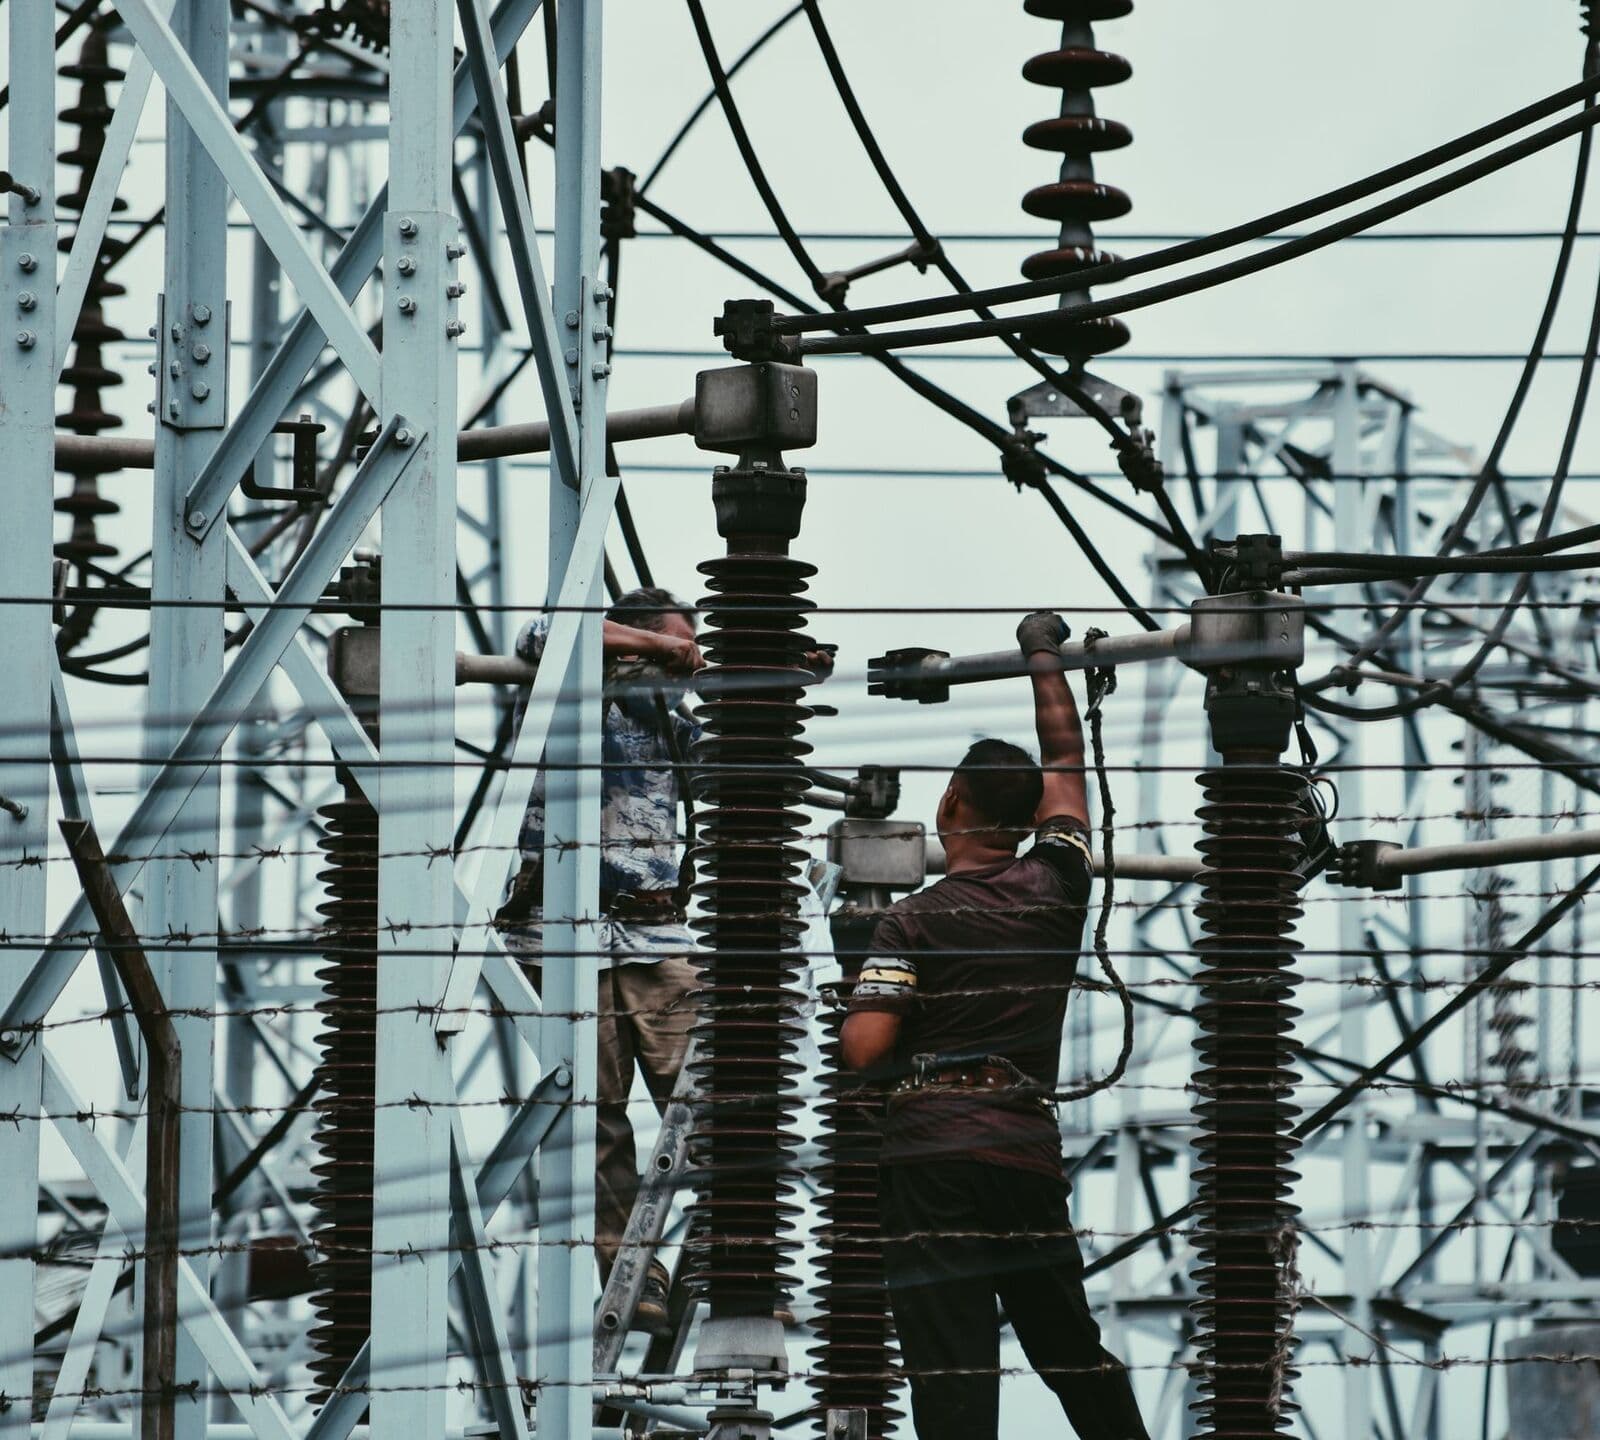
SCADA networks and remote sites can't go offline, so changes are planned around them.
SCADA and ICS. Availability outranks confidentiality here, and you often can't take a system offline to investigate what happened on it.

OSFI's technology and cyber risk rules set what an examiner will ask to see.
OSFI B-13. Technology and cyber risk across three domains: governance, technology operations and resilience, and cyber security. It binds federally regulated institutions, and only those.
What do you need from Organizational Change Management?
Tell us who you are and what you're working on. A senior engineer reads your message before replying, so the first answer is a real read on scope, risk and timing, within an hour, 24/7. Nothing here is a commitment, and we'll tell you plainly if we're not the right fit.
Your request
- Service
- Organizational Change Management
What happens next
- A senior engineer replies within an hour, 24/7, never an SDR.
- We book a 30-minute call to listen, sketch options, and flag risks.
- You get a scoped statement of work within 3 business days.
Call the 24/7 line
+1 514-465-1584Organizational change management for technology, made real.
We do the technology half of this discipline. Saying which half matters, so here it is.
The half we do, and the half we don't.
Organizational change management covers restructuring, culture, and mergers as well as systems. We don't do those. What we do is the change management plan around a deployment we're delivering: who's affected, what breaks, what training lands, and whether people use the thing afterward. That narrowness is the point. Generic OCM consulting arrives with a framework and no ability to change the system when the system is the problem. We can edit the configuration, so our first move is usually fixing the tool rather than persuading the person. Culture programmes and reorganisations are organisational work of a different kind, and they need a certified practitioner.
Where a rollout actually fails.
Most failed rollouts fail before launch, in the design. Risk sits in three places. The workflow that gets slower for the people doing it most, which no amount of communication fixes. The champion who was never asked and now owns the resentment. And training built on a vendor demo instead of your configuration, so day one doesn't match the slides. We use ADKAR to structure the work because it's the common language most Canadian PMOs already speak, not because a model substitutes for fixing the software.
Adoption gets measured or it didn't happen.
Attendance sheets and satisfaction surveys tell you people showed up and were polite. We instrument the actual system: logins, feature use, and the workaround still running in parallel. Prosci's benchmarking reports up to 135% higher benefits realisation for projects with excellent change management (Source: Prosci, 2026), and most of that gap is measurement discipline. PIPEDA applies to whatever usage data we collect, so we scope it to the minimum and tell you what's being collected before it's turned on.

Want a Senior IT Consultant's Read on Your Setup?
Tell us what you run today and what keeps breaking. A senior SMEnode engineer replies within an hour with a first read on scope, risk and timing. No sales handoff.
Request a consultHow our technology adoption work runs.
Four steps, and the first one can cancel the rollout. Readiness work sometimes finds that the deployment shouldn't ship yet, and we'd rather say so in week two than train people on something that'll be abandoned. That's an awkward conversation and it's cheaper than the alternative. The rest is unglamorous: role-based training on your real configuration, then thirty days of watching what people do instead of what they said they'd do. Whatever they work around gets fixed or gets explained.
Engagement phases
Phases 01 to 04
Read the workflow
We sit with the people who'll use it and count the clicks. Who gets slower, who gets faster, who wasn't asked. That's the change readiness pass, and it ends in a written list of what the rollout breaks.
Fix the tool first
Configuration changes before communication. If the system's worse for someone, no training plan saves it. Being able to edit the software is the whole reason this ordering works.
Train by role
A live session, a recording, and a one-page reference per role, built on your tenant rather than the vendor's demo. People learn the screens they'll actually see on Monday.
Measure and correct
Thirty days of usage data. We chase the workarounds and either close the gap or tell you why it stays. You get the usage picture, not a training completion rate.
Organizational change management questions, answered straight.
Answers first, including where we stop. An architect takes the call.
Where this work connects.
These disciplines share the same senior team and tend to land together. Follow the thread to the next one.
- AdvisoryDigital Transformation ConsultingCanadian digital transformation consulting that ends in migrated systems and retired licences, not a vision deck.
- AdvisoryIT Strategy and RoadmapCanadian IT strategy consulting that ends in a costed technology roadmap we can build, not a binder.
- AdvisoryIT Audit and AssessmentCanadian IT audit services that examine the running estate, then price every finding.